Named owners, decision rights and evidence across the AI life cycle.
A basic requirement for any AI governance platform is an accountability framework. Without the ability to plan and organise roles and responsibilities, you cannot establish accountability - and without accountability, you cannot govern AI.
That is not a secondary feature. It is the foundation.
For a South African organisation King V already expects the governing body to know who is accountable for technology that can affect people and the organisation. POPIA already names a responsible party. An accountability framework is how those duties are assigned to a named AI use, not left in a policy.
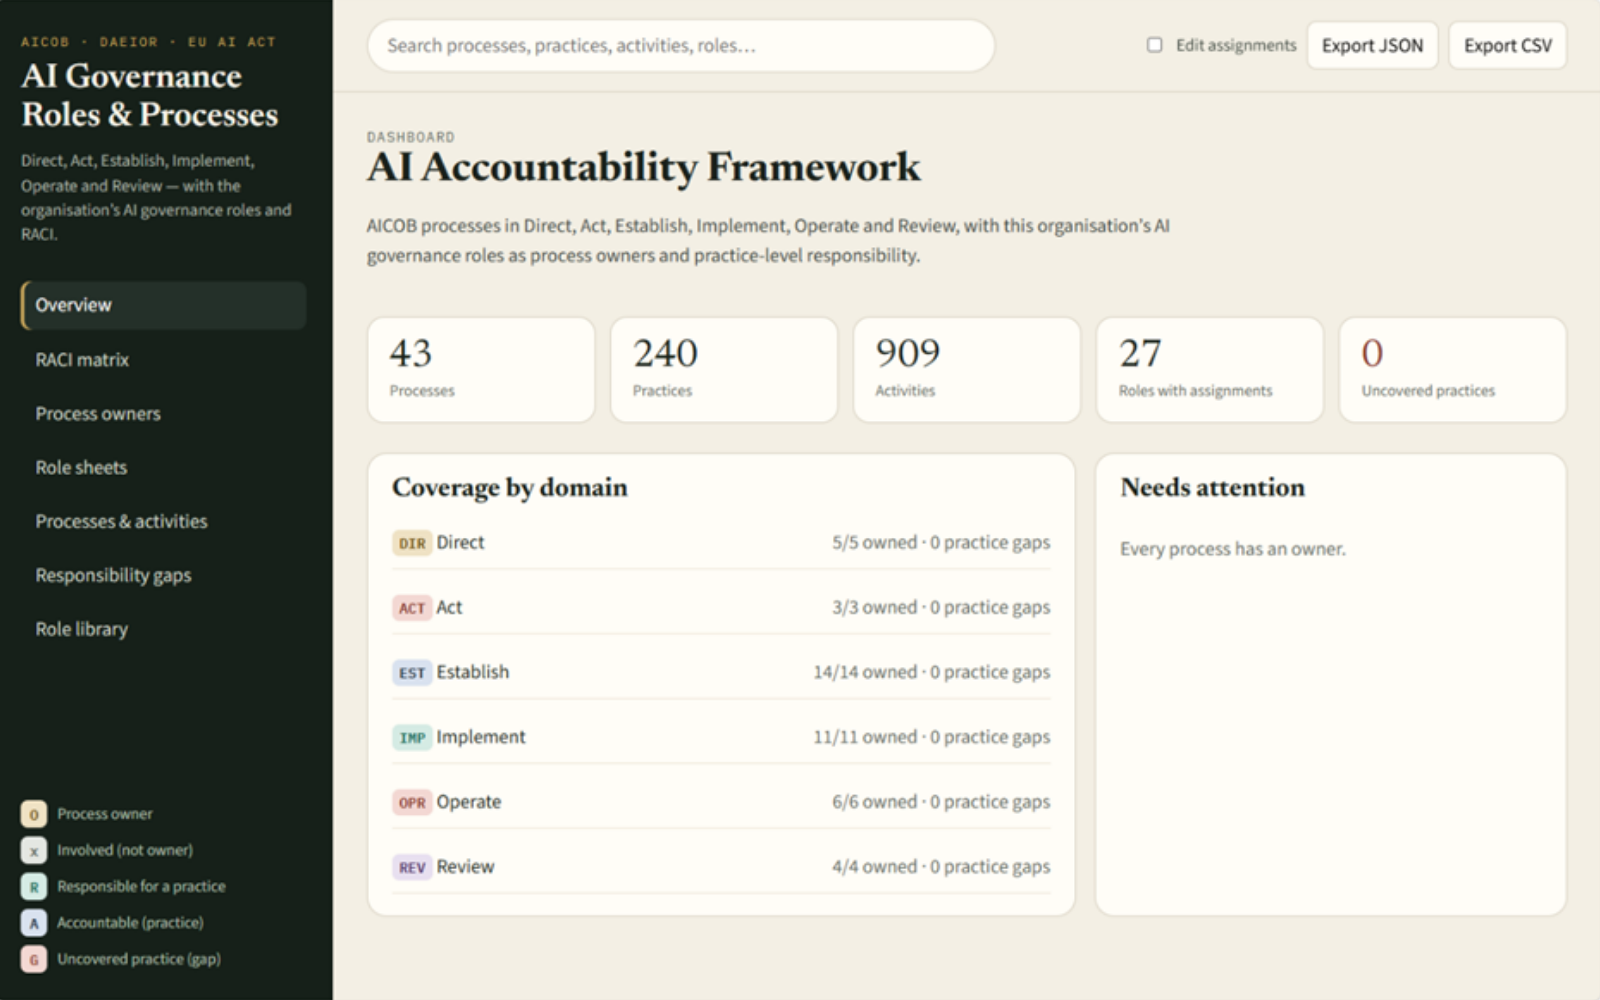
Most organisations already have AI policies. Many have risk registers, model inventories, and ethics principles. What they often lack is a working answer to a simpler question: who owns what, at which stage, and who signs off when something goes wrong?
AI does not fail the way a traditional IT system fails. A classic application usually has one owner. An AI system has several at once: a business owner accountable for the outcome, a technical owner accountable for the model and data pipeline, a risk owner accountable for residual risk, and legal or compliance accountable for regulatory obligations. If those lines are not planned and recorded, each function assumes another team is covering the gap. The result is not shared ownership. It is no ownership.
That is why an accountability framework has to come before dashboards, inventories, and control libraries. Standards already treat this as non-negotiable. NIST's AI Risk Management Framework puts accountability structures inside the GOVERN function: roles must be documented, communicated, and empowered, and executive leadership must take responsibility for deployment decisions. ISO/IEC 42001 requires the same under Clause 5.3 - roles, responsibilities, and authorities assigned across the AI lifecycle, not left implicit. POPIA adds the responsible party and, where used, the operator. The EU AI Act then adds legal identities on top where the organisation is on the Union market: provider, deployer, importer. A platform that cannot map organisational roles to those duties cannot produce an audit trail that survives scrutiny.
This is also why the capability belongs in the platform, not only in a policy PDF. Governance tools that inventory models but cannot assign owners, route approvals, or show who held which duty at the time of a decision leave the hardest part of governance outside the system of record. You cannot govern what you cannot attribute.
The failure mode is already visible in the market. Surveys keep finding the same pattern: unclear ownership of AI initiatives, governance or compliance gaps cited as a top reason programmes underperform, and boards that authorised AI use without assigning anyone to own the outcome of a specific system. Authorisation is not accountability. Permission to use AI is not the same as a named human who owns the decision the system influences.
A usable accountability framework inside an AI governance platform should therefore let you:
Until that layer exists, the rest of the platform is inventory and workflow. Useful, but not governance. Governance starts when someone can be named, the duty can be planned, and the organisation can show it.